tech
Ledger Confirms Hardware Implant Behind $86 Million Crypto Theft
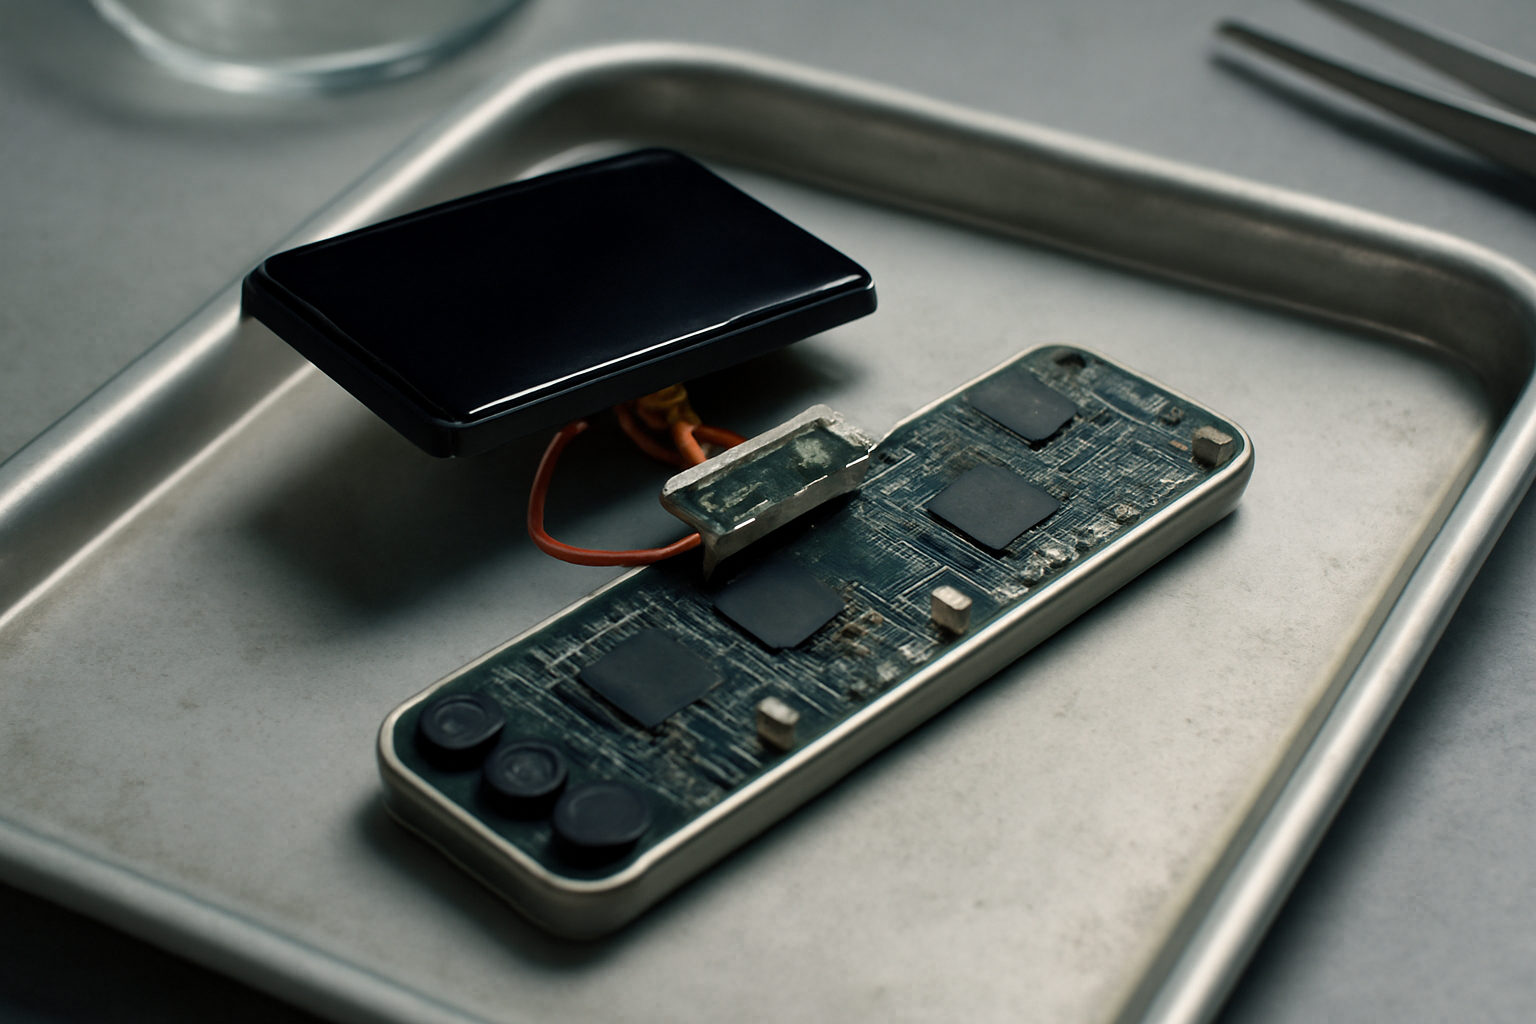
Ledger confirmed Oct. 10, 2026, that a hardware implant secretly built into some of its crypto wallets is likely behind a supply chain attack that has stolen more than $86 million from hundreds of accounts, according to The Verge. The affected devices were not sold directly by Ledger but through a third-party reseller called CryptoBillis, and Ledger has asked that reseller to pause all sales while it investigates, The Verge reported.
Owners of Ledger wallets bought outside the company's own store face the most immediate risk. There is no indication that wallets purchased directly from Ledger have been compromised, the company said, according to The Verge.
What did Ledger find inside the tampered wallets?
Ledger said "one of the impacted users' devices contained an unauthorized hardware implant," according to The Verge. Photos and videos shared on X and Threads appear to show a small circuit board hidden underneath the wallet's screen. The implant is built to intercept everything displayed on screen, including the seed passphrase a user sees once during initial setup, The Verge reported.
How did the implant steal crypto from victims?
The hidden circuit board reportedly includes an embedded SIM card that lets it transmit captured seed-passphrase data back to whoever planted it, according to The Verge. A seed passphrase works as the master key to a crypto wallet. Anyone holding it can move funds out of that wallet without a password or PIN. Once attackers had the passphrase, they could drain the wallet directly, The Verge reported.
How much crypto has been stolen, and how many people are affected?
- More than $86 million in crypto has been stolen, according to The Verge.
- Hundreds of wallets have been hit, The Verge reported.
- Ledger's own systems and directly sold wallets show no sign of compromise, the company said.
What is Ledger doing about CryptoBillis?
Ledger asked CryptoBillis to halt all wallet sales while the investigation continues, according to The Verge. The company has not said whether it will extend the pause to other resellers or confirmed that CryptoBillis has complied. Ledger has stressed the issue appears limited to this one supply chain rather than its own manufacturing or sales channel, The Verge reported.
What should Ledger owners do now?
Anyone who bought a Ledger wallet from a reseller rather than Ledger's own store, especially from CryptoBillis, should treat the device as suspect. That means checking whether the case has been opened and whether an extra circuit board sits beneath the screen, and avoiding entering an old seed phrase into hardware of uncertain origin. Setting up a new wallet only from a factory-sealed device bought directly from Ledger is the safer path until the investigation is complete. Ledger had not published a full list of affected serial numbers as of Oct. 10, 2026, according to The Verge.
For the full reporting and original images of the implant, see The Verge's story.
Questions
Were wallets bought directly from Ledger affected by the implant?
No. Ledger said there is no indication its own systems or wallets sold directly by the company have been compromised, according to The Verge.
How much crypto has been stolen in the Ledger supply chain attack?
More than $86 million has been stolen from hundreds of wallets, according to The Verge.